API penetration testing in Dallas

Manual testing of your API against the OWASP API Security Top 10, at a flat fee set by endpoint count. Every test includes fix steps for each finding and one retest within 90 days.

Authorization first

What an API penetration test covers

An API penetration test checks whether your API trusts the wrong requests. We test each endpoint by hand against the OWASP API Security Top 10, with a close look at authorization: whether one user can read or change another user’s records by changing an ID.

This test is for APIs that stand on their own, like partner integrations and public APIs. If the API sits behind your own web app, our web application penetration test already covers it up to your tier’s endpoint limit, and our mobile app penetration test includes an app’s backend up to 25 endpoints.

  • Every endpoint in scope, tested by hand
  • Authorization at object, function and property level
  • Signed-in and signed-out requests
  • One environment, set in writing
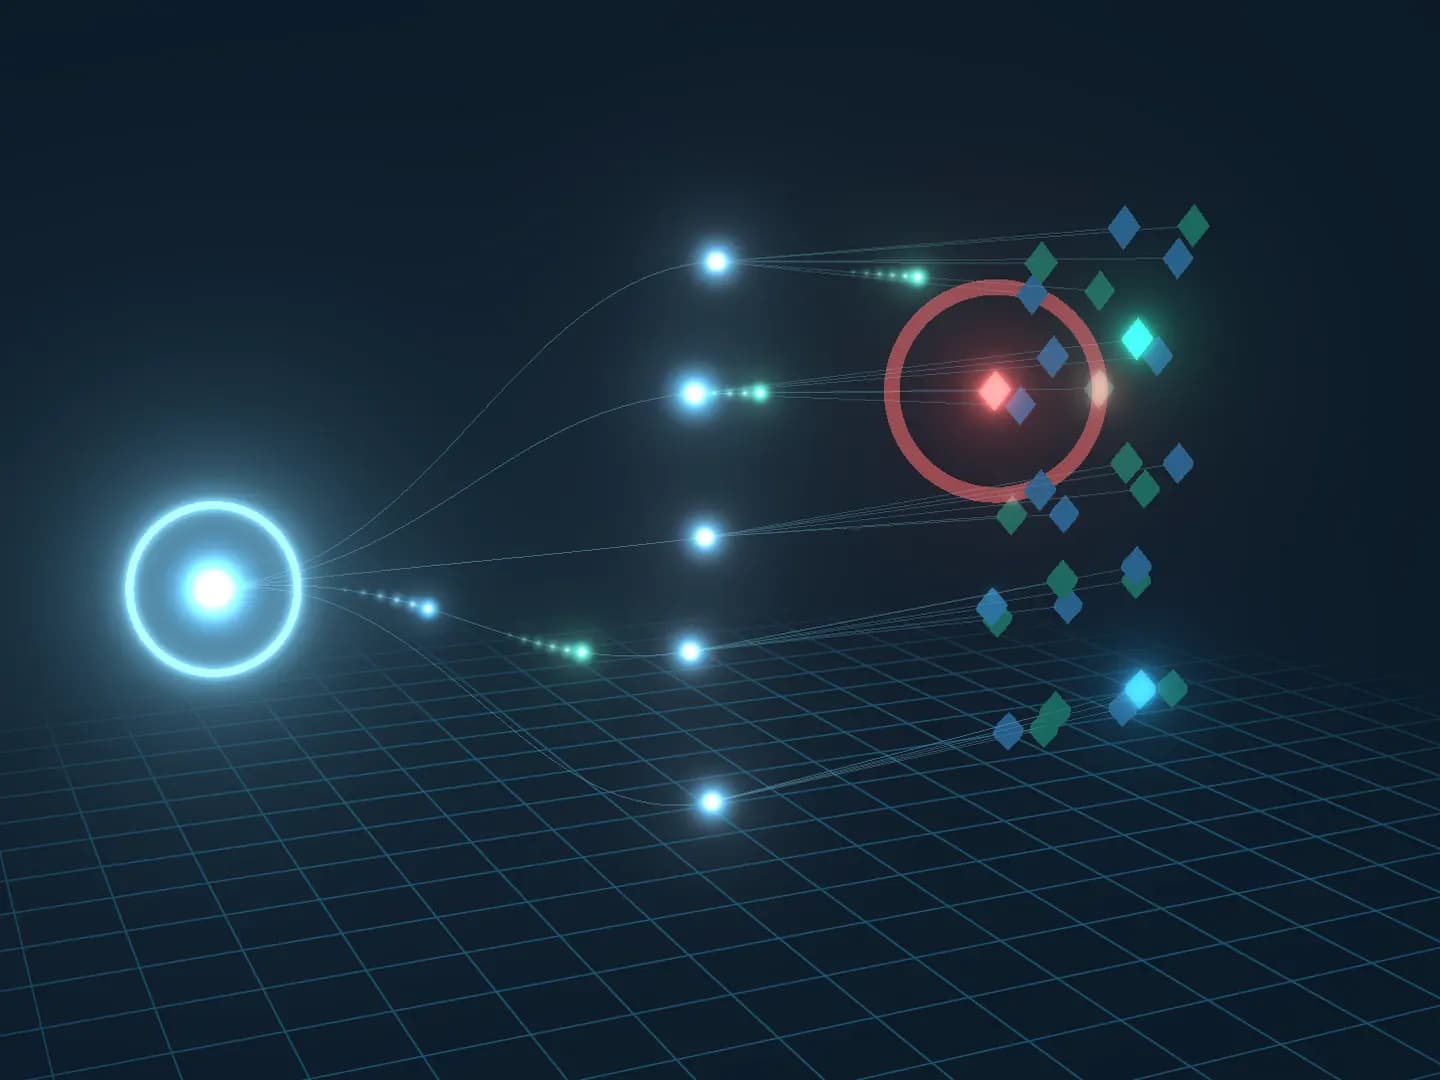
Illustration of an object-level authorization test. Not a client API.

Mapped to OWASP

What we test

OWASP ranks broken object level authorization as the top API risk, so authorization comes first. We check it at three levels: the record, the action and the individual field. Every category of the OWASP API Security Top 10 below is part of every test.

OWASP API Security Top 10 2023 categories and what the API test checks for each
OWASP API Security Top 10What we test
API1:2023Broken Object Level AuthorizationWhether one user can read or change another user’s records by changing an ID in the request.
API2:2023Broken AuthenticationToken handling, sign-in and credential reset flows, and endpoints that answer without authentication.
API3:2023Broken Object Property Level AuthorizationWhether responses expose fields a user shouldn’t see, and whether requests can set fields they shouldn’t, like a role or a price.
API4:2023Unrestricted Resource ConsumptionMissing limits on request rates, page sizes and uploads, tested within the limits your rules of engagement allow.
API5:2023Broken Function Level AuthorizationWhether a regular user can call admin or other privileged functions.
API6:2023Unrestricted Access to Sensitive Business FlowsWhether a business flow, like checkout, sign-up or booking, can be automated or abused in ways that hurt the business.
API7:2023Server Side Request ForgeryWhether the API can be made to fetch addresses it shouldn’t, including internal ones.
API8:2023Security MisconfigurationError detail, cross-origin and HTTP settings, and unneeded methods or debug endpoints left switched on.
API9:2023Improper Inventory ManagementOlder API versions and undocumented endpoints we can find that still answer requests.
API10:2023Unsafe Consumption of APIsWhere your API passes data from third-party services back to users, whether it treats that data as untrusted.

Included in every test

What you get

Leadership gets an executive summary. Your developers get every finding with its risk rating and evidence, plus the steps to fix it. We walk your team through the results on a readout call, and after your fixes are in, we retest the reported findings once.

Not included

  • Source code review
  • Fixing the findings (you get the fix steps)
  • More retest rounds, or a retest after 90 days. We quote these as a fixed fee.
  • Scoping call and rules of engagement

    We agree on the scope and the environment, then write both into rules of engagement before testing starts.

  • Executive summary

    A short read for leadership: what we tested, what we found and which risks matter most.

  • Risk-rated findings

    Every finding with its risk rating, the evidence behind it and the steps your developers need to fix it.

  • Readout call

    We walk your team through the results and answer questions about each finding.

  • Letter of attestation

    For your SOC 2 auditor or a customer’s security questionnaire.

  • One retest

    After your fixes, we retest the reported findings once, within 90 days of the report.

Flat fee

How endpoint pricing works

The fee is flat and set by endpoint count, tested in one environment. We confirm the count with you on the scoping call, so you know the price before testing starts.

Tests start at $5,290 for up to 25 endpoints. The second tier covers 26 to 75 endpoints, and above 75 we quote a fixed fee after scoping. If your API sits behind your own web application, the web application test already covers it within its tier.

API penetration testing tiers by endpoint count
EndpointsFee
1 to 25Flat fee
26 to 75Flat fee
76 or moreFixed-fee quote after scoping

How the test runs

How the test runs

The same six steps for every application test. Nothing gets tested until the scope is in writing, and nothing in the report goes unexplained.

  1. 01

    Scoping call

    We confirm the endpoint count and the environment, then your tier and the flat fee, before any testing starts.

  2. 02

    Rules of engagement

    Scope, environment and test window go into written rules of engagement. We test only what they cover.

  3. 03

    Manual testing

    We test every endpoint in scope against the OWASP API Security Top 10, signed-in and signed-out, with authorization checked at the object, function and property level.

  4. 04

    Report

    An executive summary for leadership, and every finding with its risk rating, evidence and fix steps for your developers. It arrives on the date set in your rules of engagement.

  5. 05

    Readout call

    We walk your team through the results and answer questions about each finding.

  6. 06

    Retest

    After your fixes are in, we retest the reported findings once, within 90 days of the report.

Audit, partner and customer evidence

API testing for SOC 2, partner reviews and questionnaires

Partners that connect to your API, and customers that buy from you, often ask whether it has been tested. If a SOC 2 audit, a partner security review or a questionnaire is driving the test, tell us on the scoping call. We scope the test to the API they’re asking about and write the attestation letter for it.

You can share the letter without handing over the full report. Your auditor or partner decides what evidence it accepts, and no single test makes a company compliant.

ITECS

Letter of attestation

Date:

To whom it may concern,

ITECS performed a API penetration test of for between and . Testing was manual and covered the scope set out in the written rules of engagement, measured against the OWASP API Security Top 10.

We reported findings: high, medium and low. A retest on confirmed the status of each reported finding, as listed in the retest summary.


ITECS

Redacted sample. Your letter names your application, test dates and results. Your auditor decides what evidence it accepts.

Choose the right test

Manual API testing or an API scanning tool?

Scanners are good at known patterns and cheap to run often. They can’t tell whose record is whose, and that’s the risk OWASP ranks first for APIs.

Manual API penetration testing compared with an automated API scanner
Manual API penetration testAutomated API scanner
What it findsAuthorization flaws, business-flow abuse and issues that only show up when two findings are chained.Known patterns, missing settings and outdated components.
Whose data is whoseChecks whether one user’s request can reach another user’s records.Can’t tell, because it doesn’t know your users or your business rules.
What you getRisk-rated findings with evidence, fix steps, a readout call and a retest.A long list your team has to sort through on its own.

From the report

What a finding looks like

Every finding follows the same format: what we found, the evidence, what it means for the business and how to fix it. This one shows the risk OWASP ranks first for APIs.

API-01API1:2023 Broken Object Level Authorization
High risk

Order endpoint returns any customer’s order when the ID changes

Affected
The order lookup endpoint of the demo API
What we found
The endpoint checks that the caller is signed in, but not that the order belongs to them. Changing the order number in the request returns another customer’s order, including their name, address and items.
Evidence
A request and response log showing a signed-in demo customer retrieving an order that belongs to a different demo customer. Personal data is redacted.
Business impact
Anyone with an account could step through order numbers and read every customer’s orders and contact details.
How to fix it
  1. Check on the server that the order belongs to the signed-in customer before returning it.
  2. Apply the same ownership check to update and delete requests on orders.
  3. Add automated tests that request another customer’s order and expect an access-denied error.
Retest
After the fix, requests for another customer’s order return an access-denied error. Closed.
Sample finding written against an intentionally vulnerable demo API. It is not from a client test.

API penetration testing questions

Endpoint counts, pricing, coverage and how manual testing compares with a scanner.

It’s a manual, authorized test of your API’s endpoints against the OWASP API Security Top 10. We check whether the API trusts requests it shouldn’t, with a close look at who can read or change which records.

If the API sits behind your own web application, yes. Our web application penetration test covers the app’s own API up to the endpoint limit of its tier. The API test is for APIs that stand on their own, like partner integrations and public APIs.

We confirm the endpoint count with you on the scoping call, before any testing starts. The flat fee comes from that agreed count, and above 75 endpoints we quote a fixed fee instead.

It’s a flat fee set by endpoint count, for one environment, starting at $5,290 for up to 25 endpoints. The second tier covers 26 to 75 endpoints, and above 75 we quote a fixed fee after scoping, so you know the price before testing starts.

Yes. Every API test covers the OWASP API Security Top 10, currently the 2023 edition, with authorization checked at the object, function and property level.

Not on its own. A scanner finds known patterns. Authorization flaws depend on who should see what in your business, so a tester has to check them by hand.

No. Source code review isn’t part of this test. We test the running API in one environment, from the outside and as signed-in users.

The test doesn’t include remediation. Your developers get fix steps for every finding, and we retest the reported findings once within 90 days of the report. More retest rounds are quoted as a fixed fee.

Related testing

Testing a web app, a mobile app or a network?

  • Web application penetration testing

    A flat-fee manual test of one web application and its own API against the OWASP Top 10.

    Web application testing
  • Mobile app penetration testing

    An iOS or Android app and its backend API, tested to the OWASP MASVS.

    Mobile app testing
  • All penetration testing

    Network, cloud, wireless, social engineering and red team testing, plus continuous testing between engagements.

    Penetration testing services
  • Vulnerability assessment

    A ranked list of known weaknesses across your systems and a plan to fix them, without proving attack paths.

    Vulnerability assessments

Scope your API test

Tell us about your API and roughly how many endpoints it has. We’ll confirm the count and the tier on a scoping call.